


WIRESHIELD EDGE
Protection on your own infrastructure.
Protect traffic inline on your own network with WireShield Edge (WS-X series). High performance, low latency and full control stay with you.
Highlights
-
Inline protection
The device sits in the traffic path and filters without traffic leaving your network.
-
High performance
Runs with low latency without interrupting traffic flow.
-
Full control
Policies, rules and rate limits are in your hands.
-
Bypass indicator
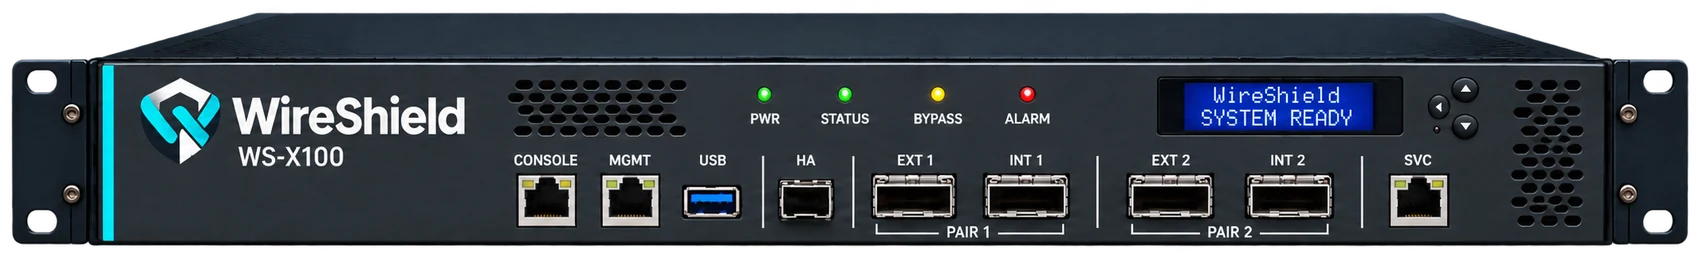
PWR, STATUS, BYPASS and ALARM LEDs on the front panel show live state.
-
HA support
A dedicated HA port enables high-availability designs.
-
Appliance Admin
Monitor CPU, RAM, temperature and fan status from the web interface.
PRODUCT FAMILY
WS-X series: from 10G to 400G
Four models, with the port speed and chassis size to match your needs. All share the same front-panel layout: console, management, USB, HA, two inline port pairs and a service port.


HARDWARE
WS-X100 front panel
The 1U chassis provides management, high-availability and two inline port pairs. The LCD shows system status right on the device.
| Port | Purpose |
|---|---|
| CONSOLE | Serial console access |
| MGMT | Management port |
| USB | USB port |
| HA | High-availability link |
| EXT1 / INT1 | Inline port pair 1 (external / internal) |
| EXT2 / INT2 | Inline port pair 2 (external / internal) |
| SVC | Service port |
Port and hardware details may vary by model revision. Contact us for the current technical specification.
FAQ
Frequently asked questions
The questions we hear most before a decision.
What is the difference between Remote protection and WireShield Edge?
With Remote protection your traffic is routed to the WireShield infrastructure, filtered there, and clean traffic returns to you over a GRE or VXLAN tunnel; no hardware needed. WireShield Edge is a WS-X series appliance that works inline on your own infrastructure, so traffic never leaves your network. Both are monitored from the central management platform.
How does WireShield Edge connect to my network?
The appliance sits inline in the traffic path: the outside of your network connects to the EXT port and the inside to the INT port of a pair, and traffic flows through the device to be filtered. The front panel has two such port pairs.
Which WS-X model should I choose?
Your line speed decides: WS-X10 (10G), WS-X40 (40G), WS-X100 (100G) and WS-X400 (400G, 2U, two NIC expansion slots). If you are unsure, describe your topology and we will choose the right model together.
Does WireShield Edge support high availability (HA)?
The front panel has a dedicated HA port for high-availability designs. Tell us your topology and we will plan the HA setup with you.
Where do I manage the device?
In the Appliance Admin web interface: CPU, RAM, temperature and fan status, ports and wire pairs, license and updates, network settings, backup, users and roles, audit log and diagnostic tools.
Where do I see attacks and reports?
The Customer Portal lists attack history with target IP, attack type, duration and impact. Reports can be downloaded.
I am under attack right now. What should I do?
Use the “Under attack?” button at the top of the page and send us the target IP/prefix and when the attack started. These requests are handled first.
Let’s strengthen your network together.
Talk to our team to find the protection model that fits your needs.